KestrelIAM
Identity visibility · by Sky Technologies

See every identity.
Including the ones nobody is aware of.

Kestrel IAM reads your identity providers, governance platforms, cloud and privileged access tools, and shows every person, account and permission across all of them on one screen. It tells you what is wrong, who should fix it, and what it could not see.

Read only · Changes nothing in your systems · First results within days
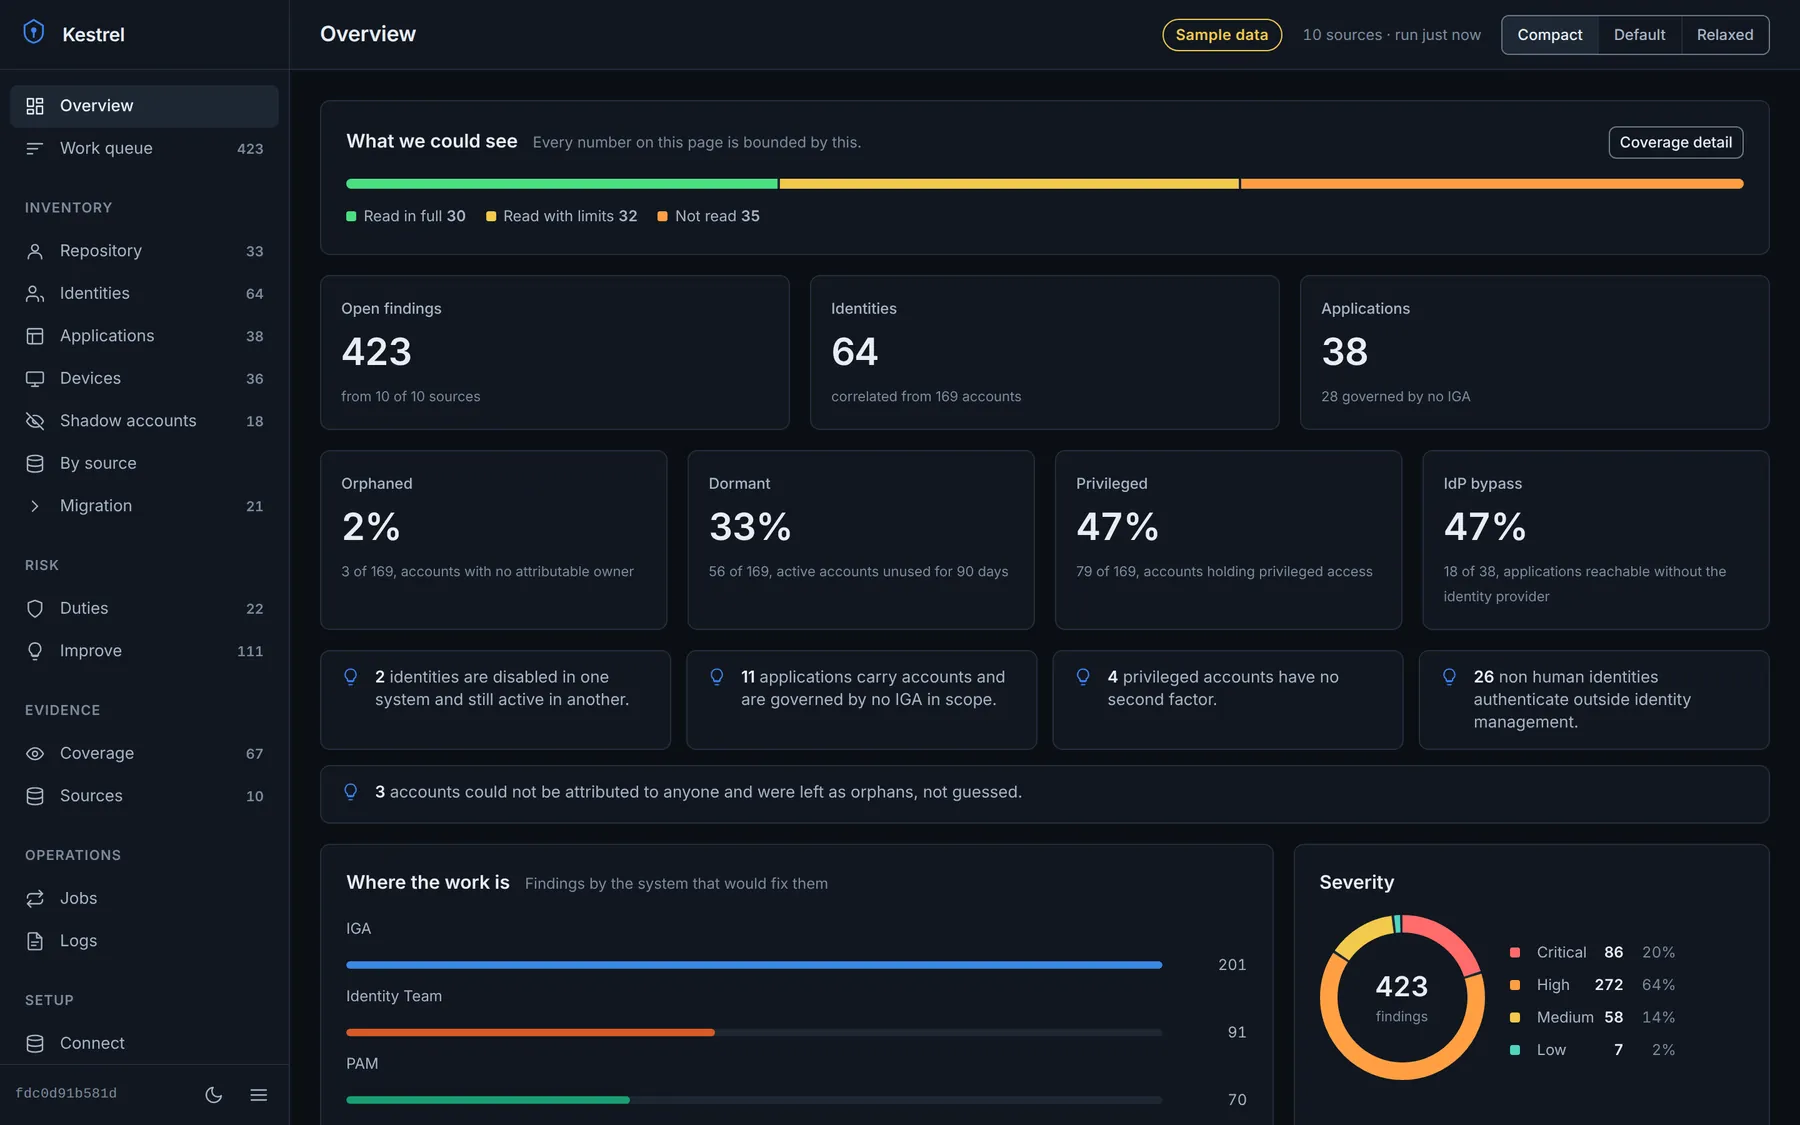
Kestrel IAM · Overview
Kestrel overview: open findings, identities, applications, orphaned, dormant and privileged accounts, with coverage of what each source could be read for

Shown with Kestrel's built in sample company. No customer data appears on this page.
Why Kestrel IAM

Your tools each see part of the picture

Identity providers, governance platforms and vaults are each right about what they manage. The risk lives in the gaps between them, and in the accounts none of them manage at all.

Accounts nobody approved

People sign up to outside services with their work login or a work email. Nobody approved those accounts, nobody reviews them, and they stay open after people leave.

Systems that disagree

A leaver disabled in one system is still active in another. A conflict of duties spans two platforms, so neither platform reports it. Each tool says everything is fine.

Reports that hide their limits

A report that says "no issues" rarely says what it could not read. Auditors, and attackers, care about exactly that part.

What Kestrel shows you

One honest view of who can access what

Every screen answers a question your auditors, your security team and your board actually ask.

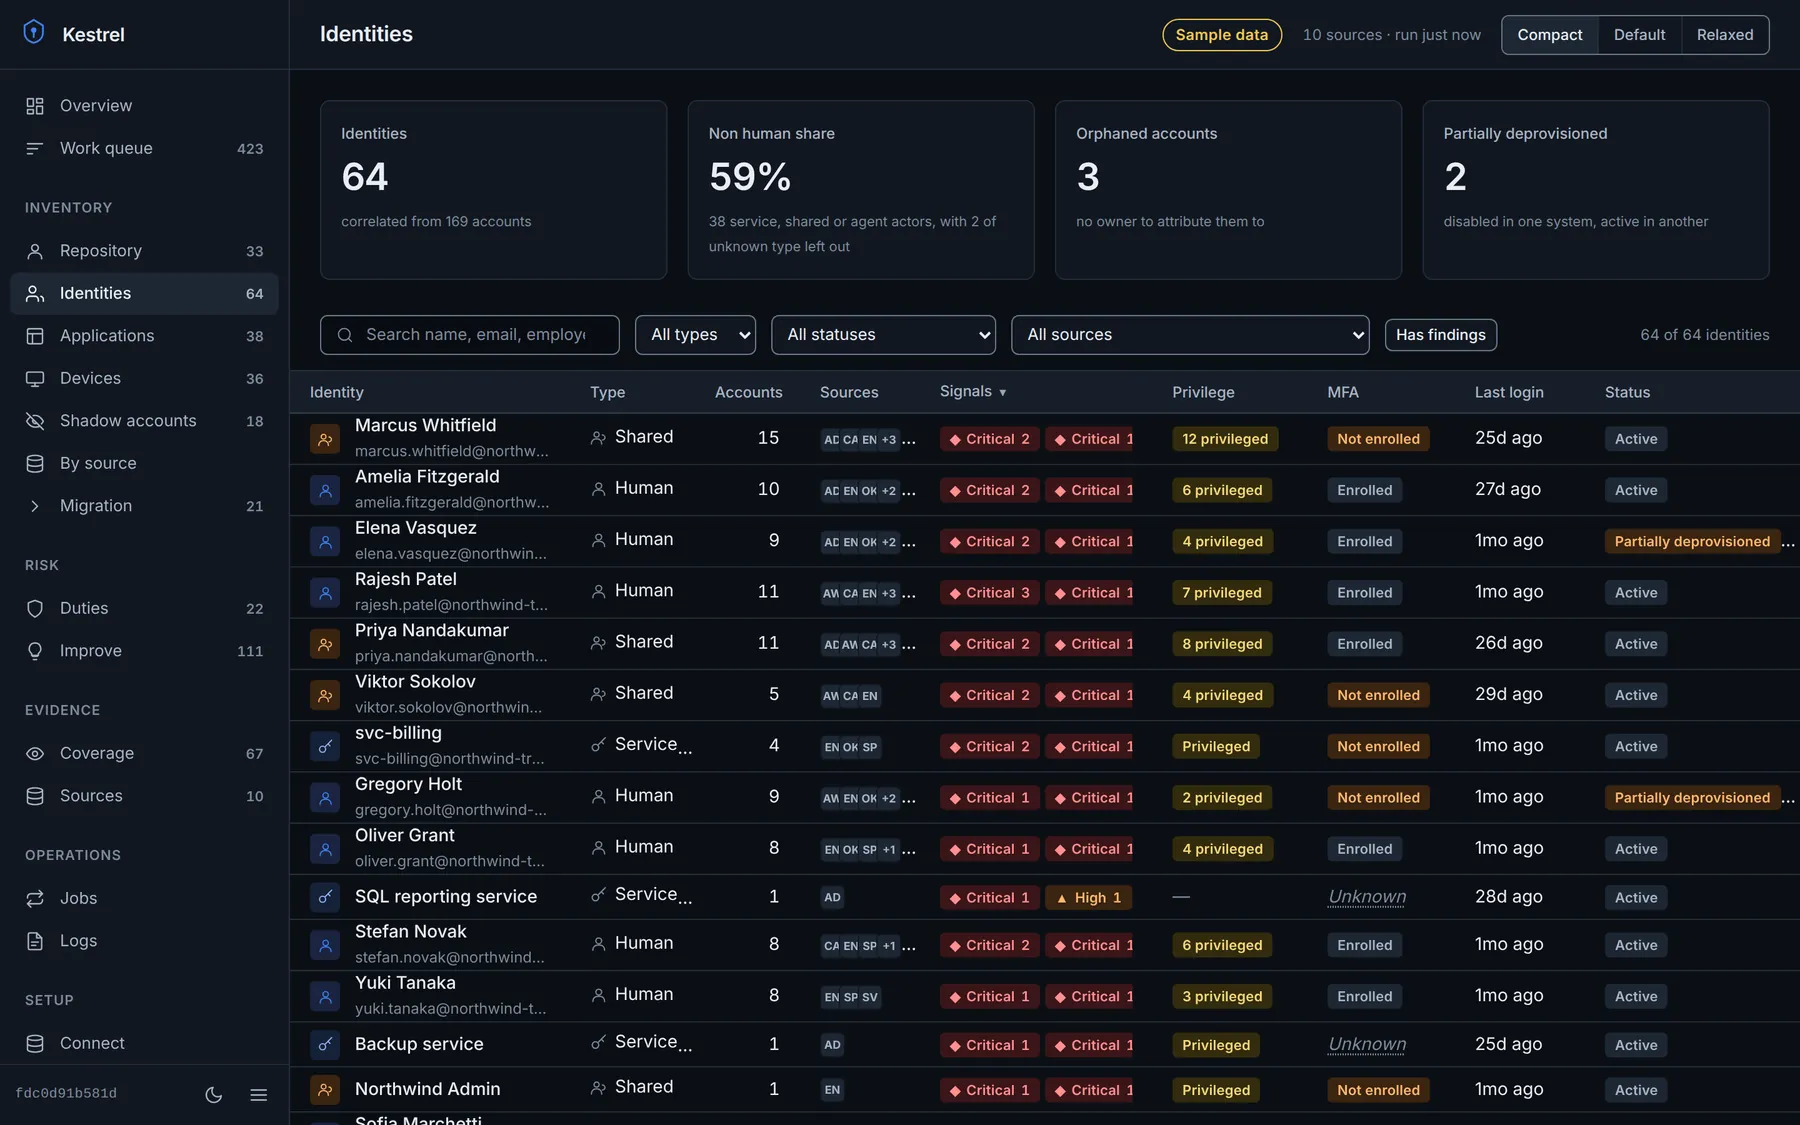
Identities

Every account, tied to the person behind it

Kestrel brings together accounts from every connected system and links them to the person, team or workload that owns them. You see each person once, with everything they can reach.

  • People, shared accounts, service accounts and AI agents, told apart
  • Leavers who are disabled in one place and active in another
  • Privileged access without a second factor
  • Accounts with no owner, flagged rather than guessed
Identities
Kestrel identities: each person with their accounts, source systems, privilege, MFA status and last sign in
Shadow accounts

The accounts outside your identity providers

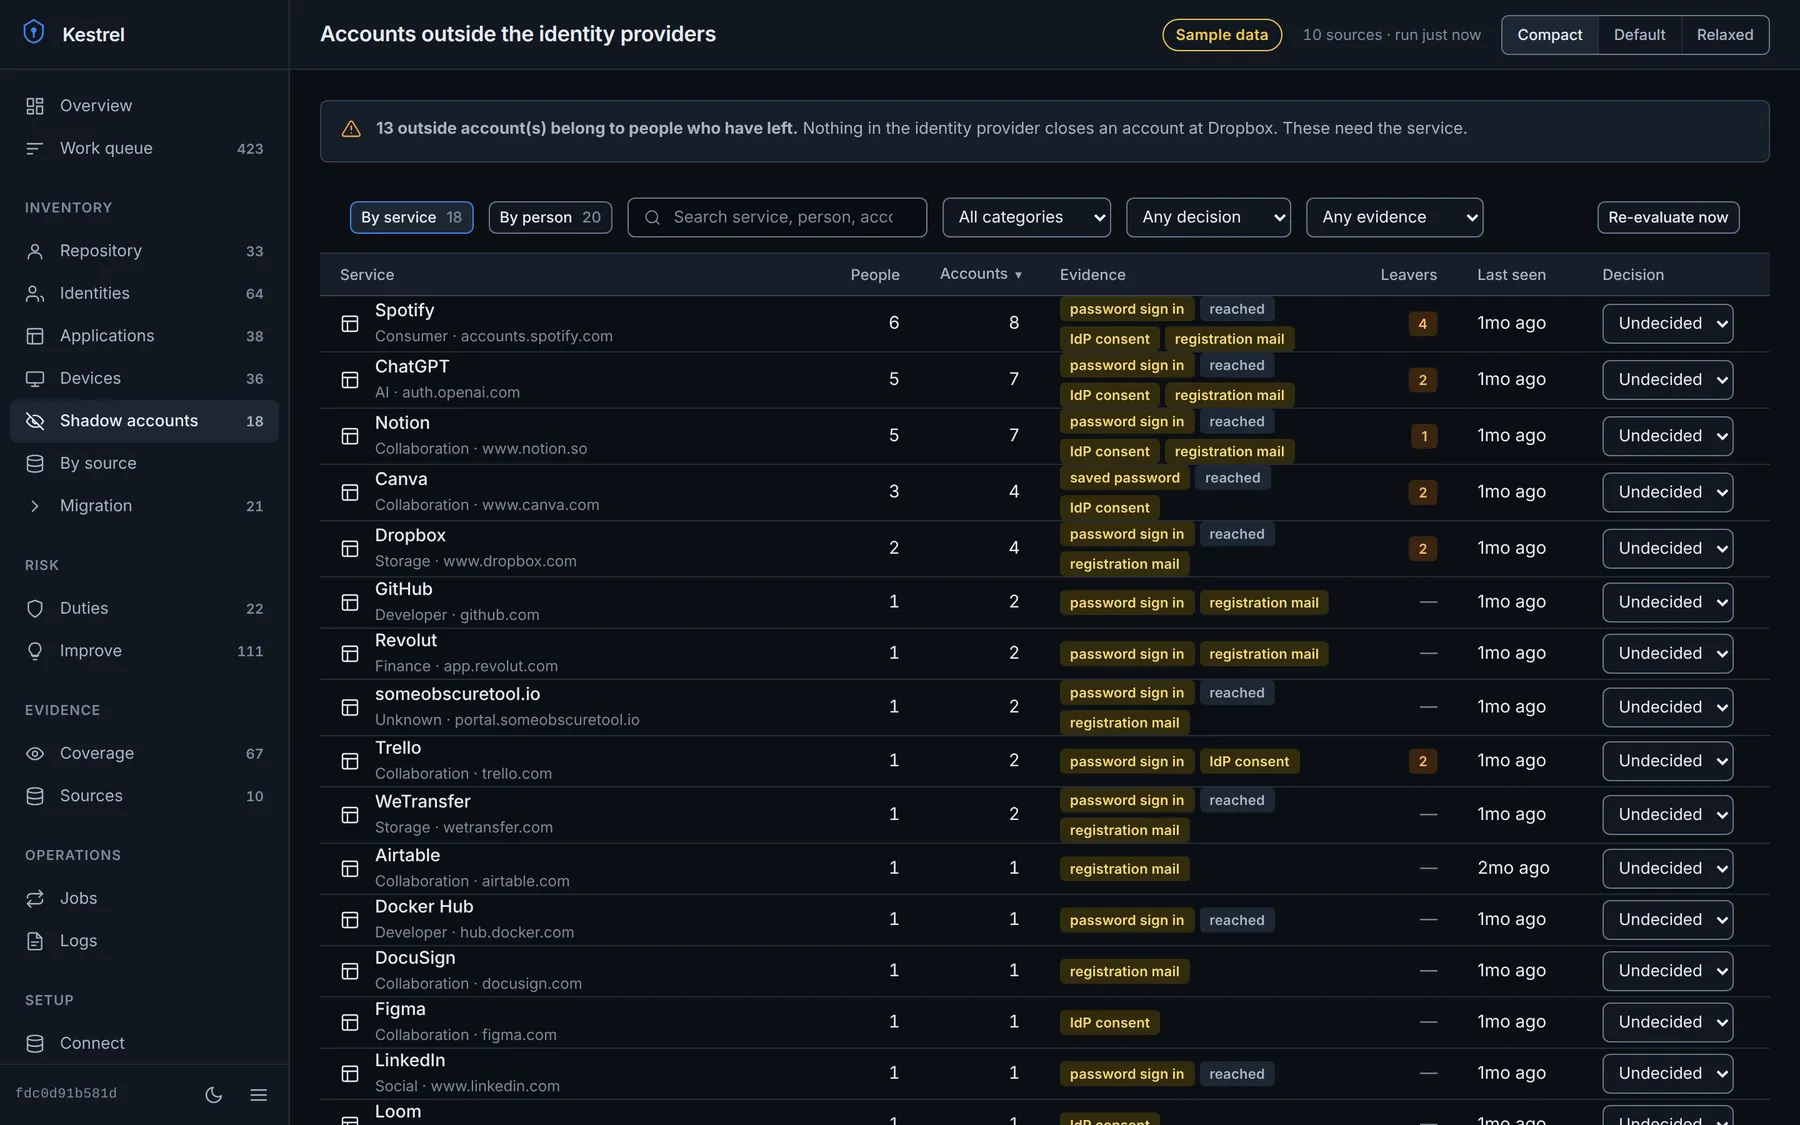
Spotify, ChatGPT, Notion, Dropbox. Kestrel finds the outside services your people opened with company identities, and shows you which of those belong to people who have already left.

  • "Sign in with Google" and "Sign in with Microsoft" approvals
  • Signals from managed browsers and cloud app discovery you already run
  • Leavers who still hold outside accounts, called out first
  • Approve, tolerate or block each service, and keep a record of the decision
Shadow accounts
Kestrel shadow accounts: outside services by number of people and accounts, the evidence for each, leavers and a decision per service
Segregation of duties

Conflicts that cross systems

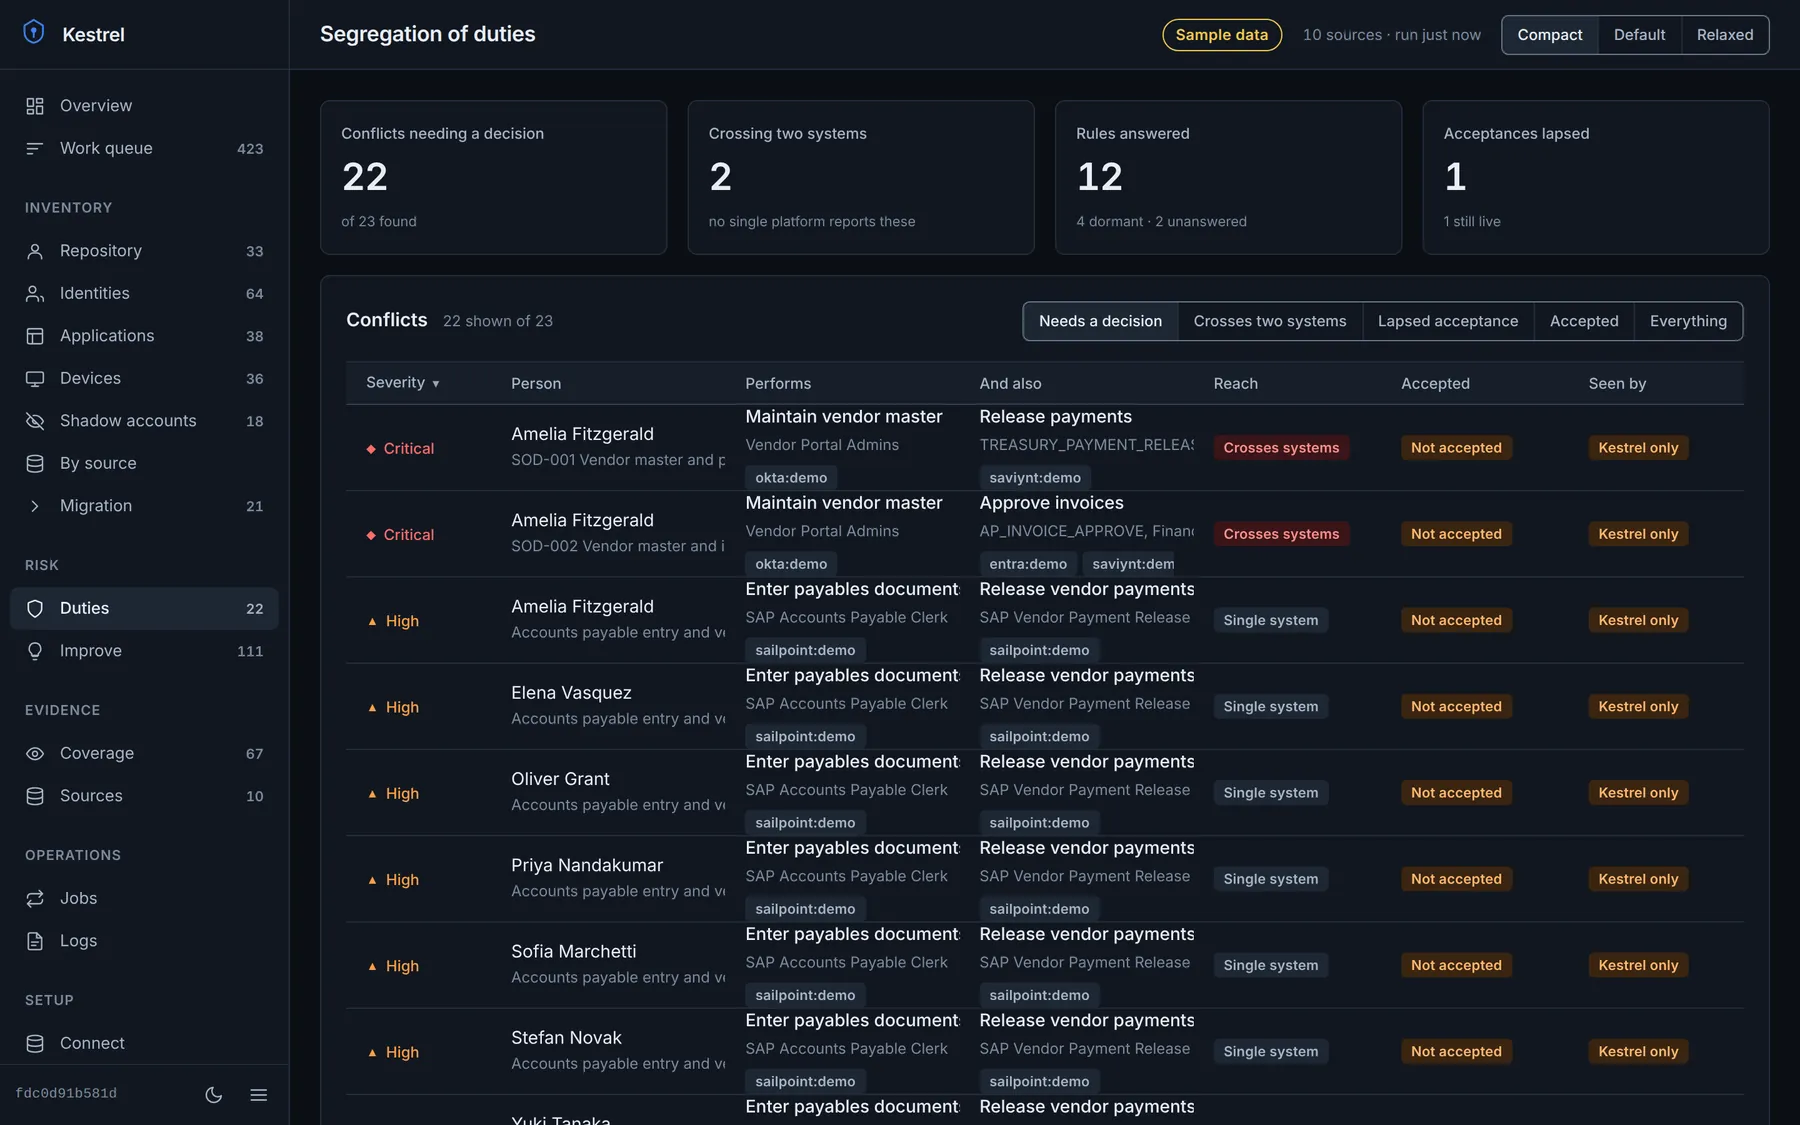
Maintaining a vendor in one system and releasing payments in another is a classic fraud path. Because the two halves live on different platforms, neither platform reports it. Kestrel does.

  • Conflicts inside one system and across two or more
  • Accepted risks with an owner and an expiry date
  • Lapsed acceptances raised again automatically
Segregation of duties
Kestrel segregation of duties: conflicts needing a decision, conflicts crossing two systems and accepted risks
Coverage

Every number says what it could not see

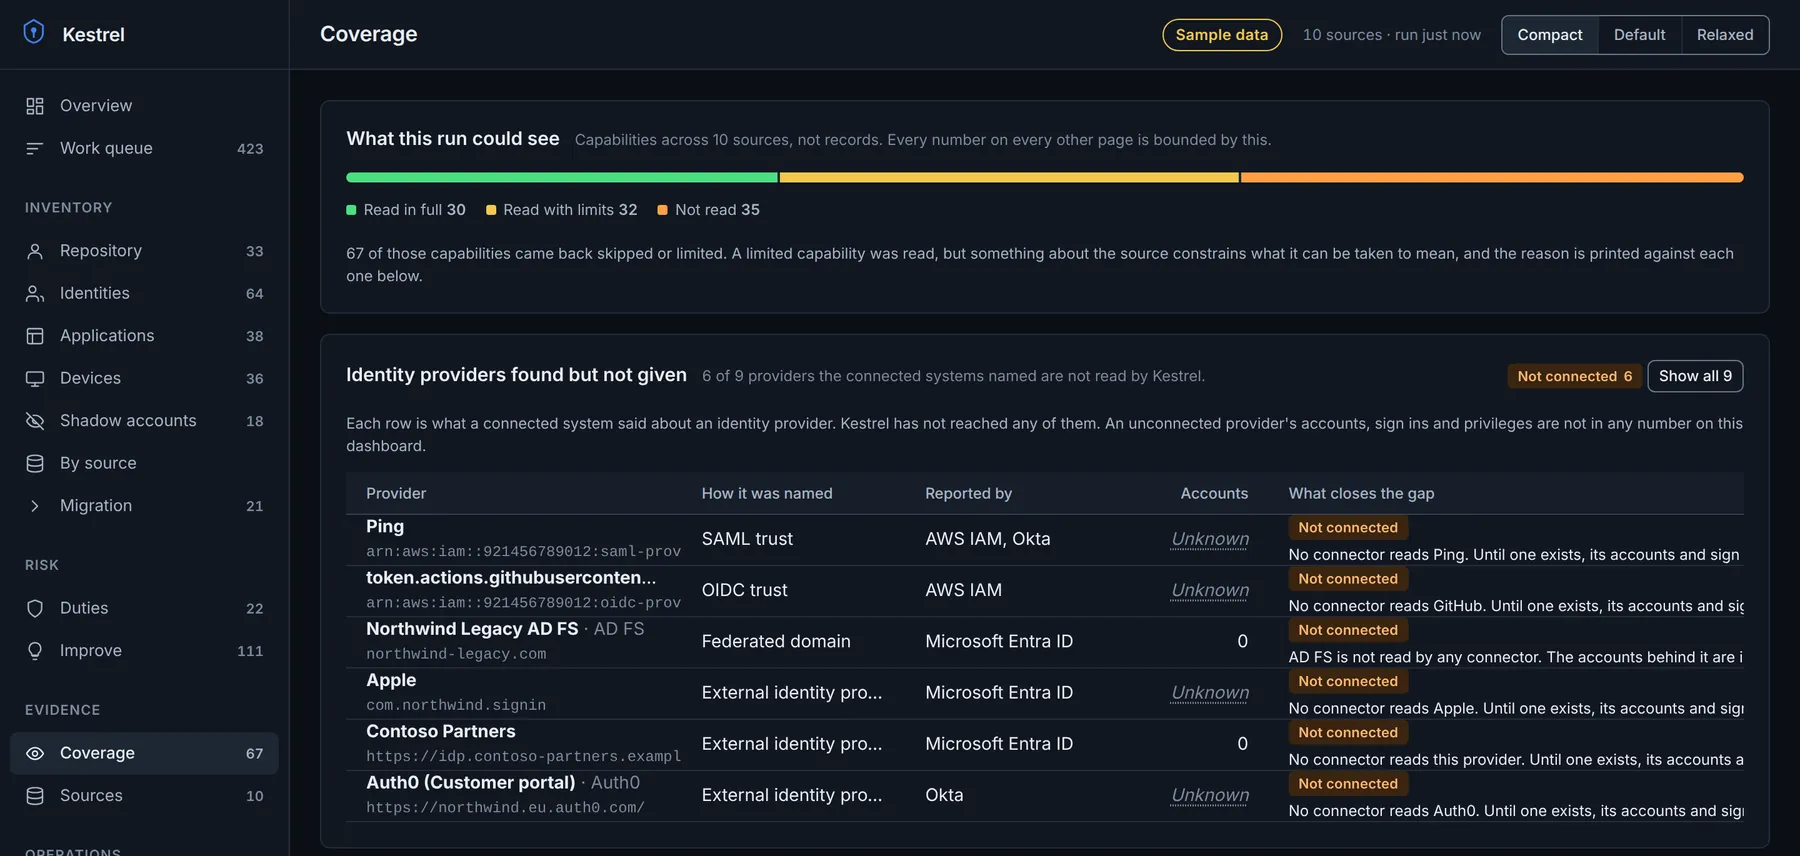
Kestrel states what it read in full, what it read with limits and what it could not read, for every source. It also lists the identity providers your systems trust that nobody has connected yet, so a blind spot never looks like a clean result.

  • Coverage shown on every screen, not hidden in a footnote
  • Identity providers your systems trust that nobody connected
  • Evidence behind every finding, ready for your auditor
Coverage
Kestrel coverage: capabilities read in full, read with limits and not read, and identity providers found but not connected
From finding to fixed

Findings go to the team that can fix them

A finding is only useful when it reaches the right person with the evidence attached.

One prioritised queue

Every finding ranked by severity and by what the account can reach, so the worst problems are at the top.

Owners and alerts

Findings are routed to your identity, governance, privileged access or application teams, with email alerts for what needs attention now.

Proof it was fixed

Each run checks again. Fixed findings close with a record of when and how, which is exactly what an audit asks for.

Integrations

Works with the stack you already have

No agents on laptops and no new identity provider. Kestrel connects to your systems with read only access.

Microsoft Entra IDIdentity provider OktaIdentity provider Google WorkspaceIdentity provider Active DirectoryDirectory SailPointIdentity governance SaviyntIdentity governance CyberArkPrivileged access AWS IAMCloud Managed browsersShadow account signal Cloud app discoveryShadow account signal

Using something else? Tell us. New sources are added regularly.

Security

Built to be trusted with your identity data

A tool that sees every account has to be held to a higher standard than the systems it reads.

  • Read only, always

    Kestrel never creates, changes or removes anything in your systems.

  • Credentials kept in a vault

    Connection secrets go into a secure credential store and are never shown again or written to a log.

  • Runs where you decide

    Inside your own environment, or operated for you by Sky Technologies as a managed service.

  • Tested like an attacker would

    Administrators and read only members, protected sign in, and penetration testing of the product itself.

What Kestrel needs from you
A typical first connection
Access levelRead only
Software on employee devicesNone
Changes to your identity providerNone
Time to connect a sourceMinutes
Time to first findingsSame day
How a pilot works

From first call to first findings

A short, fixed scope pilot on your real systems, run with our IAM architects.

1

Scope

A 30 minute call to choose the systems and the questions that matter most to you.

2

Connect

We help you create read only access for each source. Nothing is installed on your users' devices.

3

Discover

Kestrel reads your estate and builds the full picture, with coverage stated for every source.

4

Review

We walk you through the findings, the quick wins and a plan for the rest.

Questions

Frequently asked

Does Kestrel change anything in our systems?

No. Kestrel only reads. Fixes are made by your teams, or by Sky Technologies if we manage your identity operations, in the systems you already use.

We already have an identity governance platform. Why add Kestrel?

Your governance platform governs the systems connected to it. Kestrel looks across everything, including the systems your governance platform does not reach, the accounts outside your identity providers and the conflicts that span platforms.

Do we need an identity governance platform to use Kestrel?

No. Kestrel works with whatever you have, from a single identity provider to a full governance stack.

Where does our data live?

Where you decide. Kestrel can run inside your own environment so your identity data never leaves it, or be operated for you by Sky Technologies.

How is Kestrel priced?

An annual subscription based on the number of identities in scope. Ask us for a quote after the demo.

Will it help with audits and regulations?

Yes. Kestrel gives you evidence for access reviews, leaver controls, privileged access and segregation of duties, which supports ISO 27001, SOC 2, DORA and NIS2 work.

See it on your own systems

Book a Kestrel IAM demo

Thirty minutes with an IAM architect. We show Kestrel on a sample company, then talk about what it would find in yours.

  • A live walkthrough, not slides
  • Your questions answered by the people who built it
  • No obligation

Two ways to start

Book a Kestrel demo → Ask for a free shadow account scan

The scan shows which outside services your people opened with company logins. Or write to contact@skytechnologies.pl